

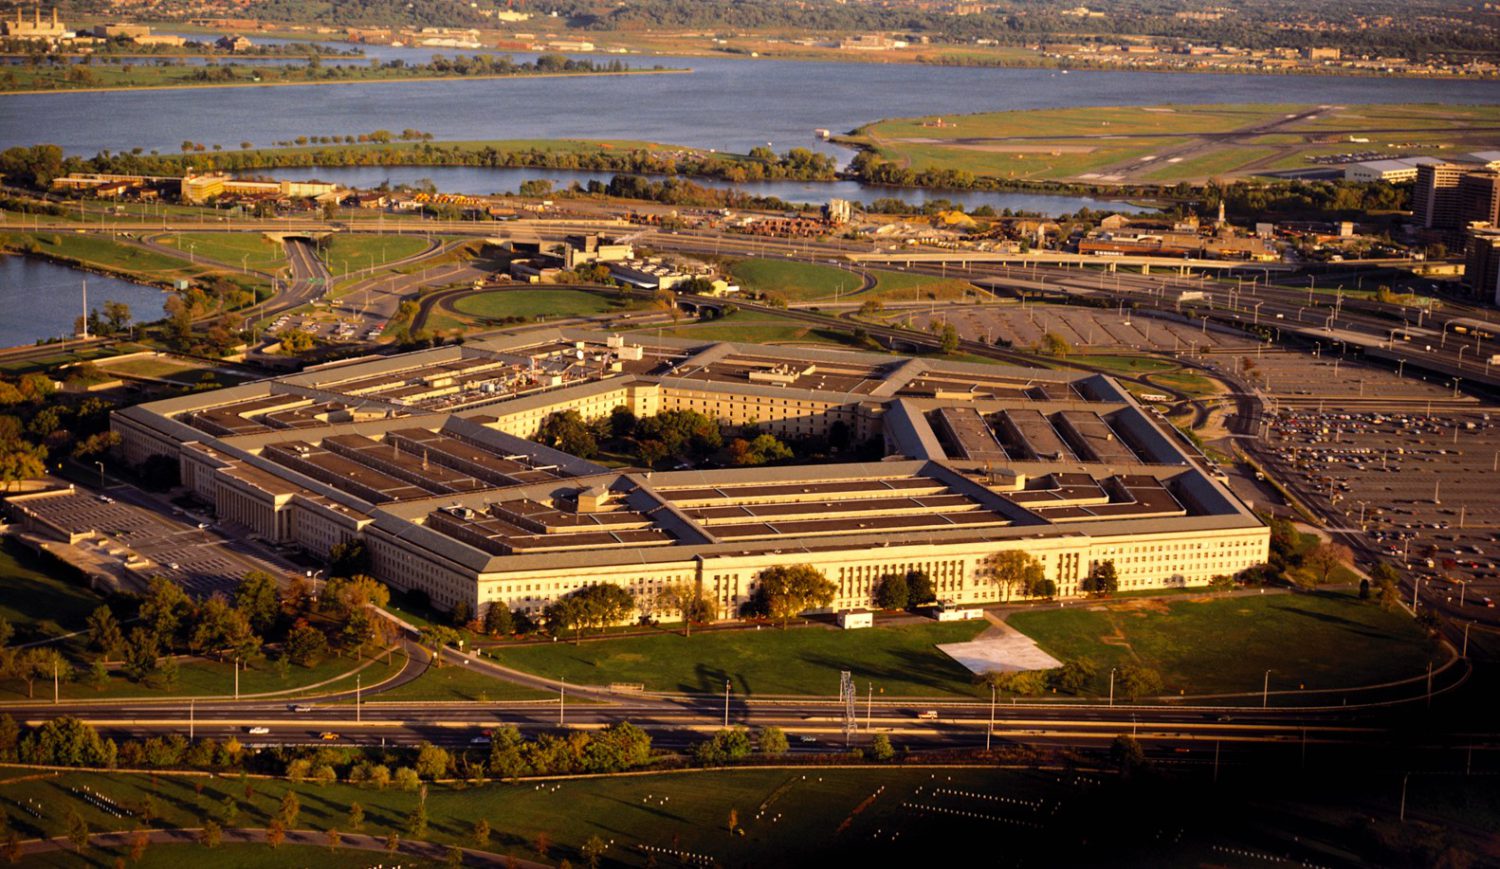
For nine months, unauthorized users had access to a Pentagon personnel database holding unencrypted Social Security numbers, military job details, and personal information on millions of service members, civilians, and veterans. The vulnerability was not discovered until July 16, 2026, according to notification letter accounts cited by SecurityWeek and Military Times.
The breach hit the Defense Manpower Data Center, one of the Pentagon’s main personnel-data repositories. According to ABC News, DMDC maintains records on more than 60 million people, covering active-duty and reserve members, civilian employees, contractors, retirees, veterans, and military families. A vulnerability in a database of that scope carries consequences well beyond a standard credential leak.
What Was Exposed
Notification letters reviewed by SecurityWeek and ABC News describe a combination of identity and employment data stored without encryption.
The compromised records could include names, dates of birth, and contact information; demographic data and Social Security numbers; and military occupational specialties and related personnel information. SecurityWeek reported that the information was stored unencrypted on the affected server, which increases the potential consequences if unauthorized users retained copies of the files.
Two Categories of Risk, One Breach
The exposed data creates two distinct risk categories: persistent identity fraud and potential operational-security concerns.
Social Security numbers generally cannot be changed the way a compromised password can be reset. For the approximately 2.76 million living people whose records were reportedly accessible, the risk of misuse can persist for years because these identifiers generally cannot be routinely replaced.
The second risk category is less familiar but potentially more serious for some individuals. Military occupational specialties combined with names and contact information may help threat actors pursue targeted social engineering. That means tailored approaches to specific people in specific roles, not mass phishing blasts. This is risk analysis based on the nature of the exposed fields, not a documented outcome of this incident.
Nine Months, Then a Patch
Unauthorized access reportedly ran from October 2025 through mid-July 2026 before DMDC discovered and patched the affected system.
Unauthorized access began in October 2025 and continued until the vulnerability was discovered on July 16, 2026, according to notification letter accounts cited by SecurityWeek and woodtv.com. DMDC patched the affected file-sharing system after discovery and initiated privacy and cybersecurity incident-response procedures.
Affected individuals were reportedly offered up to one year of credit monitoring and identity-protection services, per woodtv.com reporting.
What Officials Have Not Said
Key questions about attacker identity, discovery method, and the scope of actual data exfiltration remain publicly unanswered.
As of available reporting, officials had not publicly identified who was behind the unauthorized access. Available reporting also does not explain how the vulnerability was discovered, and it remains unresolved whether every accessible file was actually copied. Access to files does not confirm that every record was exfiltrated.
Defense officials told ABC News they have found no evidence the compromised information has been misused. That is the government’s current assessment, based on available evidence, not a determination that misuse will not occur.
What Affected Individuals Should Know
Credit monitoring is a floor, not a ceiling, for anyone whose records may have been in the affected system.
If your records are in that system, one year of credit monitoring is a starting point. Social Security numbers and employment histories do not reset, and the risk of fraud or targeted deception can persist long after the initial exposure. Monitoring your credit reports beyond the offered period and staying alert to unusual contact claiming military or government affiliation are reasonable precautions.
The affected file-sharing system has been patched. Patching the vulnerability does not establish whether previously accessible data was copied or retained by unauthorized users.