

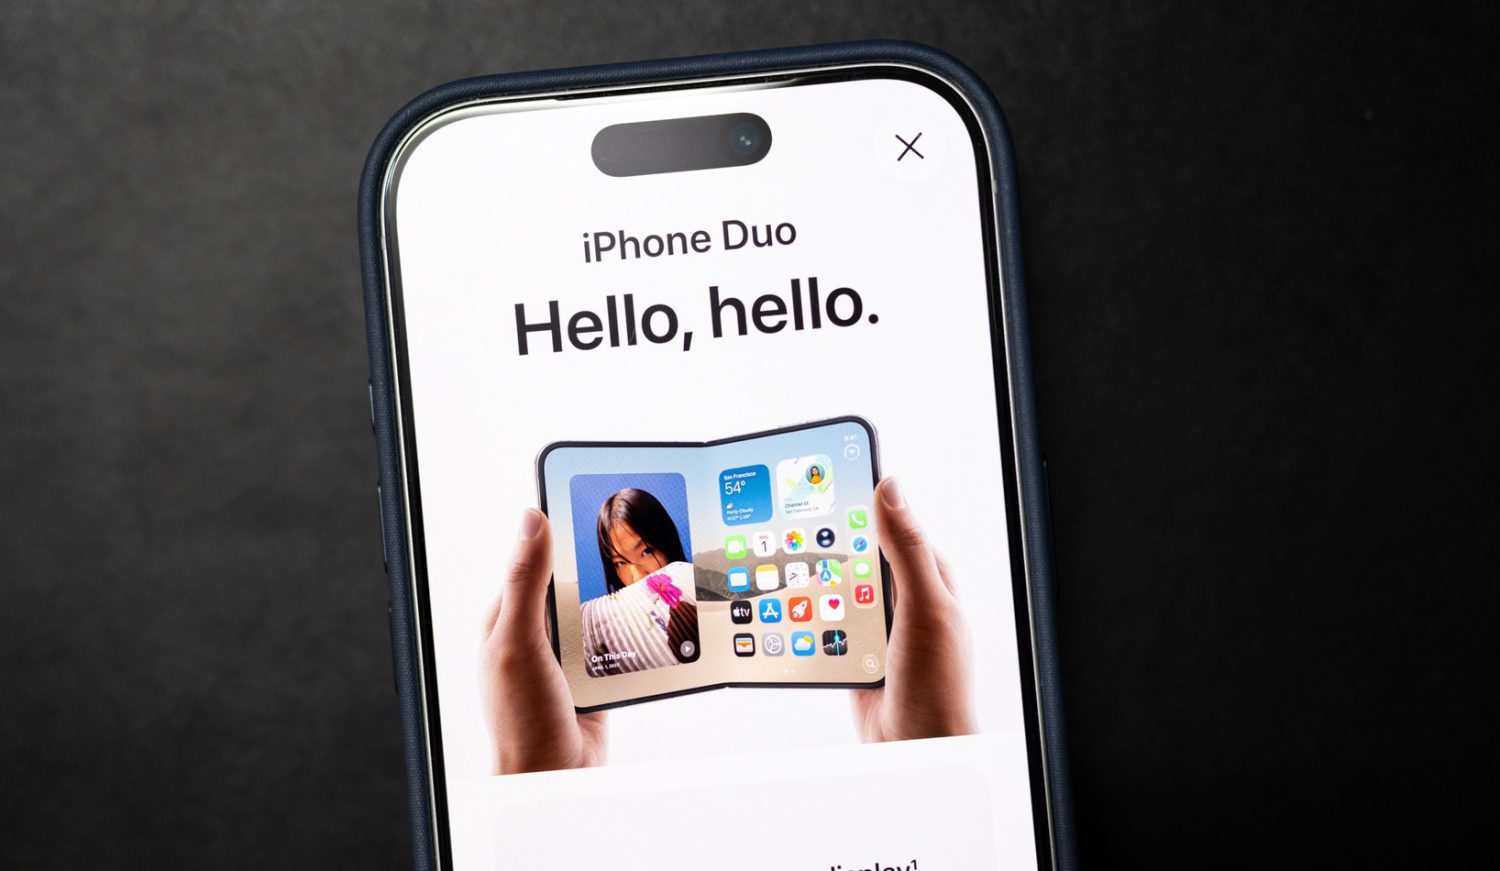
Before Apple’s official preorder window even exists, a scam already does. Security researchers at Malwarebytes have identified a fraudulent Apple-branded page for the iPhone Duo that deploys the DarkSword exploit chain against vulnerable devices. If successful, the attack can expose saved passwords, Apple Notes content, device information, and cryptocurrency-wallet data. Apple’s official preorder window does not open until October 16, 2026, and availability begins October 23.
The part worth underscoring: you do not have to tap “buy,” submit a form, or approve a prompt. On certain unpatched iPhones, loading the malicious page alone may be enough to begin the exploit attempt.
What the Fake Page Promises
The bait is a $500 voucher and an Apple-quality design. The hook sets before you notice anything is wrong.
The page copies Apple’s visual style closely, complete with a countdown timer and a “$500 Authorized Partner Exclusive” voucher used to create urgency. Nothing about the presentation immediately signals fraud to someone who just wants to be first in line for a $1,999 foldable iPhone.
According to Malwarebytes, the DarkSword exploit chain embedded in the page targets older iPhones running vulnerable iOS 18 releases. The precise version boundary differs slightly across reports. That is exactly why applying Apple’s latest available security update matters more than checking whether your specific version number appears on any list.
How to Spot It Before It Spots You
What looks like an official Apple page and what gives it away are two different things.
The clearest red flag is the timeline. Apple’s published schedule puts preorders no earlier than October 16; any page claiming to offer an official Apple preorder before that date cannot be part of Apple’s published schedule. Malwarebytes also found that the fake page references “natural titanium” and screen sizes inconsistent with the iPhone Duo’s published specifications, small details that a careful reader would catch and a rushed one might not.
Apple branding, copyright text, and product photography on a page prove nothing about who actually owns that domain. The only reliable path to a legitimate preorder is one you initiate yourself: type Apple’s address directly into your browser, open the Apple Store app, or visit a known carrier or retailer. Do not follow preorder links from unsolicited emails, text messages, advertisements, or social media posts.
A $500 voucher attached to a $1,999 product, arriving from an unknown source, is not a deal. It was the reported bait used to lure visitors to the malicious page.
If You Already Opened the Link
The situation is serious, but the steps forward are clear.
Update your iPhone to Apple’s latest security release and restart the device as a precaution. Apple has confirmed that security fixes addressing DarkSword-related web attacks are available through its security updates, per Apple Support. Do not wait to see whether anything seems wrong first.
If you entered passwords, payment details, or any personal information on the page, change those credentials from a separate trusted device. Start with your Apple Account and email, then move to banking and any cryptocurrency accounts. Review recent activity across all of those accounts, and contact your bank or card provider directly if payment information was submitted.
What Comes Next
More campaigns targeting iPhone Duo buyers are possible as the October 16 preorder date approaches.
Similar campaigns may appear as October 16 gets closer, potentially arriving through paid advertisements, cloned retailer pages, and unsolicited messages timed to reach people at peak excitement. The safest preorder is one you control from the start: navigate to Apple’s site yourself, open the Apple Store app, or walk into a known carrier. No voucher is worth the exposure.