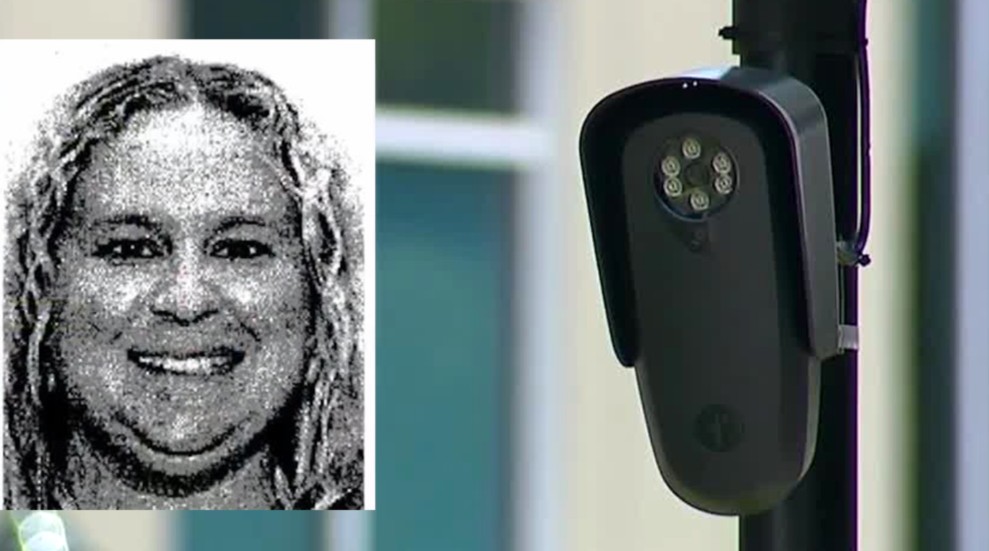
Every time her husband ran a search, the system recorded it as hers. Former Savannah Police Officer Amber Harpe acknowledged giving her department-issued Flock Safety username and password to her husband, a federal ICE agent who did not have an independent Flock account through the Department of Homeland Security. Between January and July 2026, those searches added up to 983 entries across six states, all attributed to Harpe in the audit log.
Assistant Police Chief Robert Gavin made the accountability problem explicit in internal disciplinary materials. The searches being conducted for law-enforcement purposes did not authorize Harpe to share her personal credentials, because the audit trail then identified Harpe rather than the actual user.
Nearly 1,000 Searches, Six States, and a Demographic Pattern
The scale of the activity, and who was being searched, became central to the department’s case for termination.
The internal audit covered January through July 2026 and identified 983 search entries tied to 97 license plates from vehicles registered in Georgia, New Jersey, Maryland, Florida, South Carolina, and North Carolina. South Carolina plates dominated the activity: 48 plates connected to 788 individual searches.
Department records noted that most vehicle owners identified in the audit were Hispanic. That demographic pattern, combined with the husband’s ICE role, would later factor into supervisors’ written concerns about how city resources were used.
Harpe’s husband maintained the searches served legitimate federal law-enforcement purposes, specifically locating ICE targets with active arrest warrants, and denied any personal misuse. Savannah officials, according to the disciplinary record, did not concede that point explicitly; their stated position was that legitimate investigative intent did not authorize circumventing the department’s access controls.
The structural problem is straightforward. When a person operates under someone else’s credentials, the audit record stops identifying who actually conducted the search. It identifies the account holder instead.
A Department That Does Not Do Immigration Work, and a Split Over Punishment
Supervisors disagreed sharply on the appropriate penalty, but the outcome was termination.
Savannah’s stated position, as reflected in departmental materials, is that the department does not participate in federal immigration enforcement. Maj. Michelle Halford noted in the disciplinary record that the demographic pattern in the audit, combined with the husband’s ICE role, raised concerns that city resources may have supported immigration enforcement without authorization.
Internal supervisors disagreed on how to respond. Interim Maj. Max Nowinsky recommended an eight-hour suspension. He cited Harpe’s clean disciplinary record and the absence of evidence that she gained personally from the access.
Halford and Gavin supported termination, arguing in disciplinary materials that the credential sharing was intentional, repeated over months, and extensive in scope. Termination took effect September 26.
Harpe subsequently filed a Civil Service Board appeal, then withdrew it without disclosed explanation; the scheduled hearing was canceled.
Investigators found no violation of Georgia’s automated-license-plate-reader statute, according to the research brief. The disciplinary basis was an SPD policy prohibiting employees from allowing unauthorized persons to access department or city software. The Harpe case was also one part of a broader SPD investigation into alleged Flock misuse by other employees, including searches reportedly connected to romantic partners or personal interests.
What the Case Reveals About Credential Sharing vs. Data Sharing
The Savannah incident exposes a specific gap between lawful interagency data access and individual credential sharing.
An agency may have authority, under applicable law and data-sharing agreements, to exchange law-enforcement information with a federal partner through established channels. That process preserves a record tied to an authorized user. Credential sharing is different: it routes another person’s activity through someone else’s account, erasing the record of who actually ran each search.
Agencies and surveillance app vendors may now face pressure to add technical controls to close that gap. Multifactor authentication and anomaly detection are among the measures that would make undetected credential sharing significantly harder to execute.