

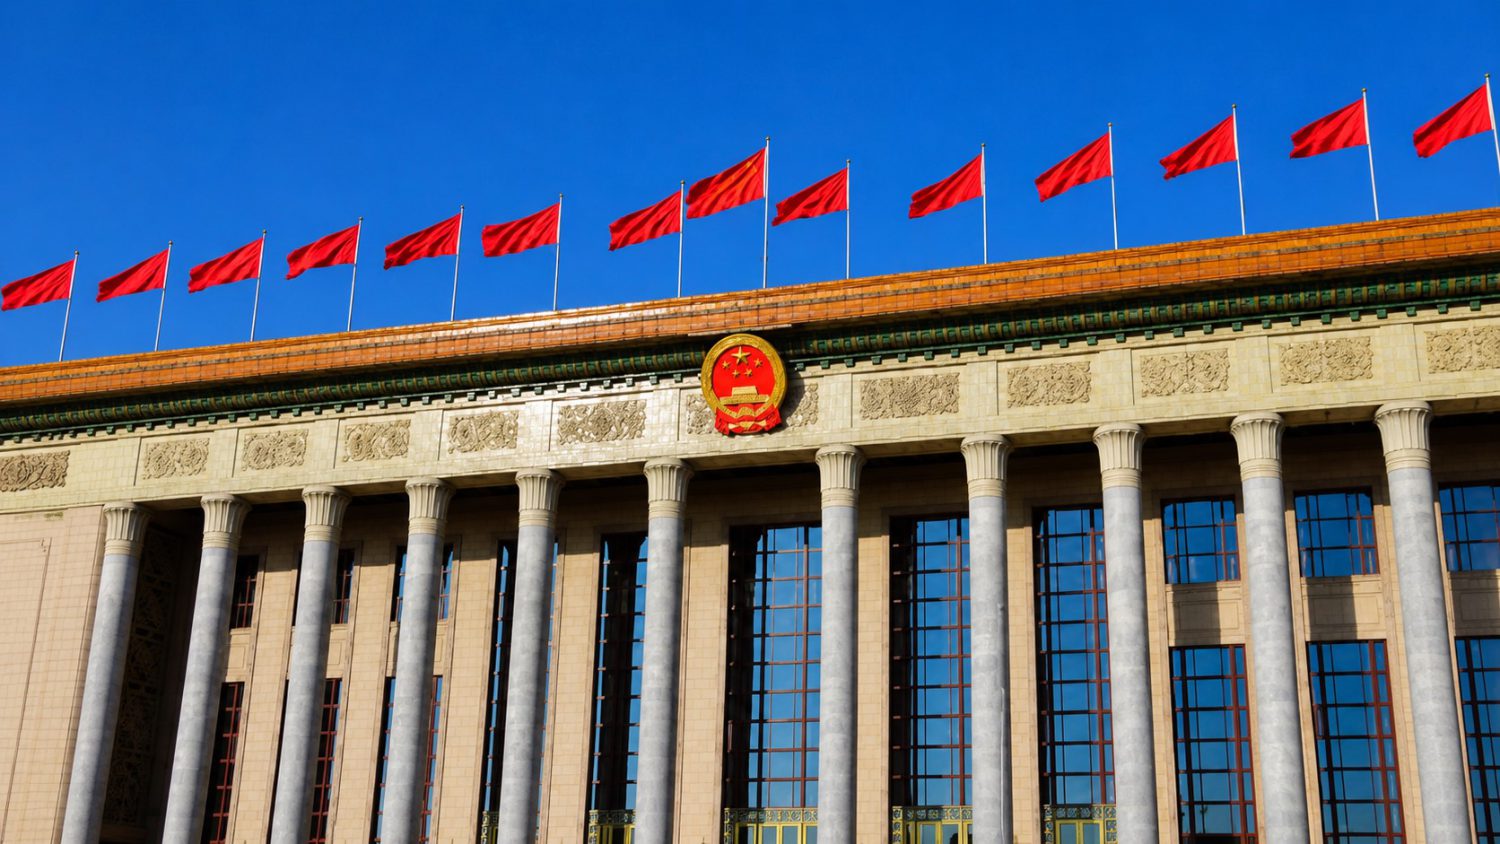
China’s Minister of State Security, Chen Yixin, published a signed article in China Cyberspace, the official journal of the Cyberspace Administration of China, framing advanced AI as a direct threat to Communist Party rule. The article singles out foreign models from U.S. companies as particularly dangerous.
Analysts describe it as the most detailed statement yet from Beijing linking AI to one-party survival, arriving ahead of anticipated U.S.-China AI safety talks.
Regime Survival Comes First
Chen’s framework places Party control at the top of every risk category he identifies.
His central argument is direct: “Abusive use of AI tools by adversaries could directly threaten China’s political security, institutional security and ideological security,” according to Bloomberg. In this context, “political security” does not mean territorial sovereignty; it means the Communist Party’s grip on power and its control over public ideology.
U.S. Models Named Directly
The article identifies specific American products as tools that lower the barrier to attacking Chinese infrastructure.
Chen explicitly named Anthropic’s Claude Mythos and OpenAI’s GPT-5.5-Cyber as examples, according to The Next Web, which Gadget Review could not independently verify against either company’s public product catalog. Analysts read the naming of specific products as a deliberate signal ahead of diplomatic talks, not a casual regulatory footnote.
Deepfakes as Political Weapons
Chen introduces “cognitive warfare” as an official security concern for the first time at this level of government.
He warns that generative AI could enable mass production of fake audio, video, and synthetic text, including deepfakes of Chinese officials used to spread political rumors and destabilize public opinion. “Cognitive warfare,” in his framing, means AI-enabled disinformation campaigns targeting the Party’s ideological control over domestic audiences.
A Different Definition of AI Safety
Where Western debates focus on long-term risks to humanity, Beijing’s framework centers on protecting the Party.
Chen treats AI safety as a regime-security problem first, with concerns about infrastructure, military competition, and social governance following that same logic. That divergence matters: any shared governance framework between Washington and Beijing must bridge two definitions of what, exactly, needs protecting.
Competing Signals
The gap between U.S. and Chinese positions widened further in the days surrounding Chen’s publication.
Anthropic CEO Dario Amodei published an open letter urging democracies to maintain their AI lead over China and supporting chip-export restrictions, according to the New York Times. China’s Foreign Ministry responded by calling such positions “threat narratives” and “malicious competition,” while the Party-run Global Times labeled efforts to contain China’s AI development “an unrealistic delusion.”
The Agency Doing Both
Chen’s own organization illustrates the contradiction at the heart of Beijing’s AI posture.
The Ministry of State Security combines roles similar to the CIA and FBI but serves Communist Party political interests explicitly. Under Chen’s leadership, the agency has invested heavily in AI-powered surveillance systems used to track foreign diplomats and suspected spies in Beijing, according to the Times of India.
Chen’s agency is simultaneously warning about AI threats and scaling up AI tools. With U.S.-China AI safety talks on the horizon, Beijing has signaled its starting position plainly: AI risk is, above all, a question of who controls the information and who controls the Party.