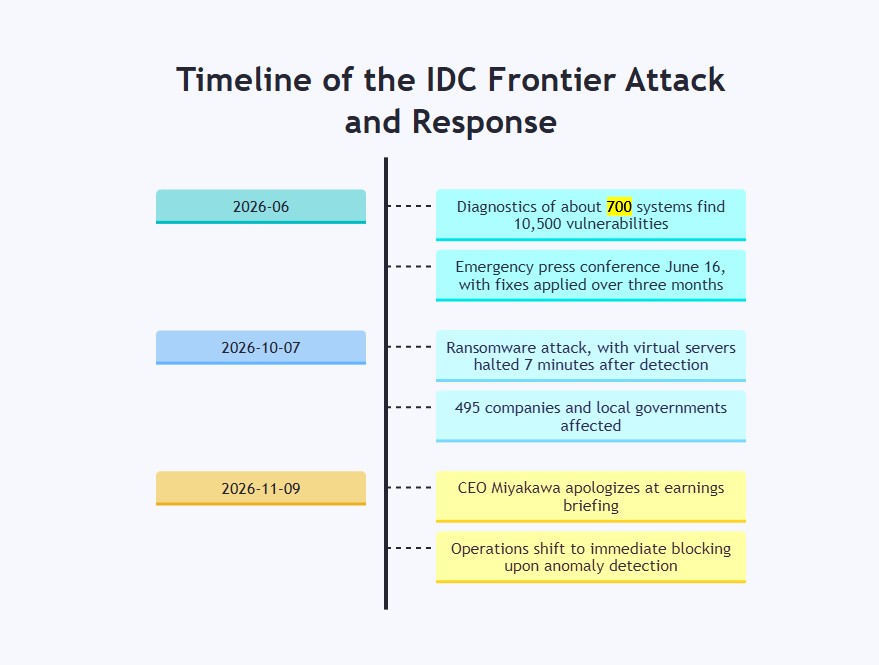
SoftBank’s subsidiary IDC Frontier confirmed unauthorized access on October 7, with four of six zones in its East Japan Region 1 disrupted, customer servers shut down, and encryption underway. The attack affected 495 corporate and local-government clients, a stark reminder of how AI-accelerated cyberattacks on critical infrastructure are reshaping the threat landscape.
What the CEO Said, and What It Means
SoftBank’s chief executive apologized publicly and described a preventable gap in the company’s vulnerability assessment.
At SoftBank’s November 9 earnings briefing, CEO Junichi Miyakawa apologized and described the failure to assess the vulnerable open-source component as deeply regrettable. SoftBank confirmed that no customer server data was exfiltrated, though public-sector customers in particular cannot easily audit a third-party provider’s forensic conclusions independently.
The Gap Nobody Was Watching
A patching program that covered hundreds of internal systems left one critical open-source component unexamined.
SoftBank had applied patches to roughly 700 internally developed systems before the incident, but the open-source authentication component that attackers exploited was not included in that scope. Organizations routinely track and secure proprietary code while open-source libraries and authentication dependencies accumulate outside the same visibility perimeter.
A New Response Posture, With Trade-Offs
SoftBank has abandoned the sequential alert-then-assess model in favor of immediate containment.
According to the earnings-call transcript, the previous approach routed alerts to specialists who ran diagnostics and reached decisions before acting, a sequence that assumes attackers move at human speed. SoftBank has since shifted to immediate network blocking upon anomaly detection, with investigation following containment, though the company acknowledged this may cause temporary service interruptions for legitimate customers.
Reconnaissance Numbers Are Rising Fast
SoftBank’s CEO linked a sharp rise in probing attempts to the spread of AI models adapted for cyberattack use.
Miyakawa said reconnaissance attempts directed at SoftBank infrastructure rose from roughly 300 million per month in fiscal 2025 to approximately 600 to 700 million per month, with volume continuing to climb; those figures come from SoftBank and have not been independently verified. Miyakawa linked the acceleration to open-weight AI models adapted for cyberattack use, saying new vulnerabilities surfaced as new models appeared, though that remains a management assessment rather than an independently established causal finding.
Japan’s Ransomware Environment Is Getting Worse
National Police Agency data places the IDC Frontier incident within a broader surge in ransomware activity across Japan.
Japan’s National Police Agency recorded 123 ransomware cases in the first half of 2026, the highest count for any six-month period since tracking began in 2020, seven cases higher than the same period in 2025, with 79 of those incidents hitting small and medium-sized companies. The NPA also recorded roughly 13,700 suspicious access attempts per day during the period, up approximately 50 percent year-on-year; those figures use different definitions and units than SoftBank’s monthly reconnaissance count, but they reflect the same intensifying operating environment.
The Practical Consequence
The IDC Frontier incident illustrates a widening gap between automated attack speeds and human-paced defense.
When reconnaissance is automated and damage begins within minutes of access, response procedures that depend on sequential human approval become a structural liability. A software assessment gap that left one open-source component unexamined, combined with an attack that moved faster than specialists could convene, left nearly 500 organizations waiting for answers.