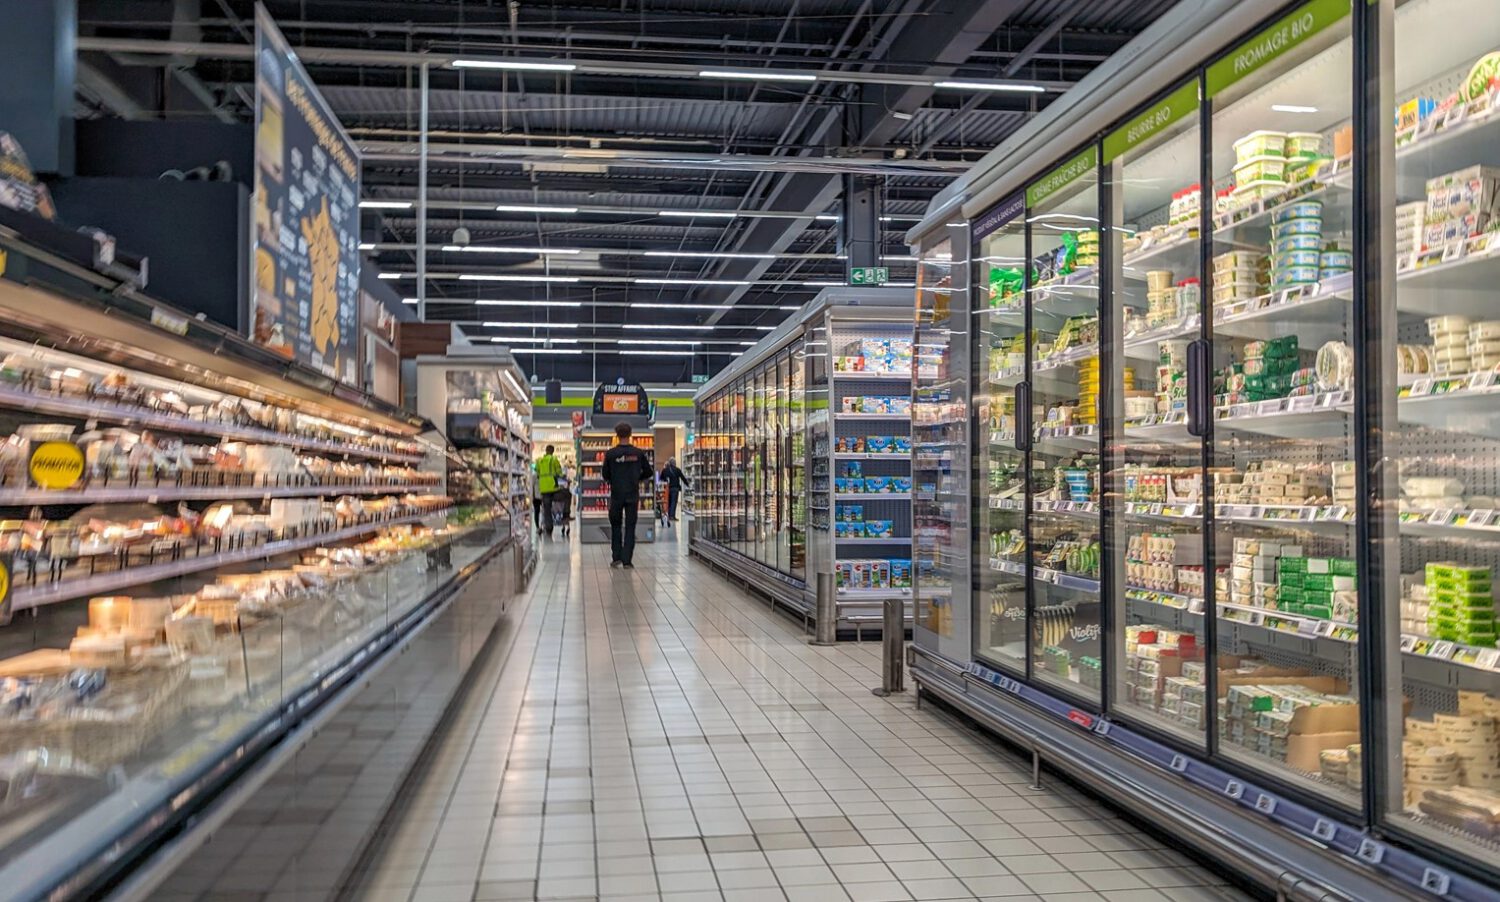
Over the nights of October 11 and 12, refrigerators and freezers at roughly 700 French retail locations stopped working as intended. The disruption triggered food spoilage, approximately 20 fires, and widespread supply failures across stores operated by Carrefour, Monoprix, Intermarché, and Coopérative U.
Paris Points Directly at Tehran
French Foreign Minister Jean-Noël Barrot publicly attributed the attack to Iran’s Islamic Revolutionary Guard Corps, describing it as “unprecedented in both scale and aggression.”
Barrot publicly named Iran’s Islamic Revolutionary Guard Corps as the alleged perpetrator. Prosecutors separately identified the Shahid Kaveh cyber unit, which they describe as affiliated with the IRGC’s Electronic and Cyber Center, as the group under investigation.
Prosecutors Open a Formal Case
The Paris prosecutor’s office has opened a judicial investigation and is seeking international arrest warrants for the head of the Shahid Kaveh group and two deputies.
The Paris prosecutor’s office announced a formal judicial investigation into the alleged attack. Investigators are pursuing international arrest warrants for the leader of the Shahid Kaveh group and two of his deputies.
How Attackers Got In
Investigators say attackers used exposed web interfaces and disabled safety alerts to disrupt cold-storage equipment across hundreds of locations.
According to investigators, Iran-linked hackers accessed refrigeration equipment through web interfaces and initiated abnormal or indefinite defrost cycles. They also disabled temperature safety alerts that would normally signal staff when units exceeded safe thresholds. French authorities cited Persian-language activity within the attack infrastructure and IP addresses linked to devices in Iran as elements of their attribution case.
Outdated Equipment Made It Easier
Cybersecurity experts say many targeted units ran obsolete firmware, making the attack accessible rather than technically sophisticated.
Cybersecurity experts assessing the incident noted that a number of the affected refrigeration units were running outdated firmware with web interfaces that were not adequately secured. That made the operation technically accessible rather than especially sophisticated, according to NBC News reporting.
The Damage Spread Beyond Supermarkets
A subsequent wave reportedly struck more than 100 establishments across Europe, including French blood banks that had to relocate stored blood products.
A separate, subsequent wave of refrigeration failures reportedly affected more than 100 establishments across Europe. Among those affected were French blood banks, which were forced to move blood products to alternative cold-storage facilities.
U.S. Military Sites Saw Similar Failures
Pentagon investigators are examining comparable refrigeration failures at American military commissaries, with Iran listed as one possible suspect, according to NBC News.
Similar refrigeration failures at U.S. military commissaries have drawn the attention of Pentagon investigators, who are treating those incidents as suspected cyberattacks. Iran is listed among the possible suspects under examination, according to NBC News reporting.
Paris Summons the Ambassador, Warns of Sanctions
France has called in Iran’s ambassador and warned of European-level consequences; Tehran has routinely denied conducting malicious cyber operations.
France summoned Iran’s ambassador to the foreign ministry following Barrot’s public attribution and warned of consequences at the European level, including potential sanctions. Iran has routinely denied involvement in malicious cyber operations, and the Iranian mission to the United Nations did not respond to comment requests in the reporting reviewed.
Part of a Wider Pattern
The refrigeration attacks have emerged during a broader period of suspected state-linked cyber disruption, though attribution for individual incidents remains under active investigation.
The incident joins a broader period of suspected state-linked cyber activity touching transportation, water infrastructure, and maritime targets. Attribution for individual incidents varies and each remains subject to ongoing investigation, a pattern also visible in the use of a surveillance app built to target political dissidents.