

Attackers hijacked Microsoft’s verified X account on Oct. 1–2, 2026, and used its 13 million followers to promote a Clippy-themed cryptocurrency token the company never authorized. Microsoft confirmed the breach, removed the unauthorized posts, and stated plainly that it has no connection to the token.
The incident worked because it stacked credibility signals: a verified blue-check account and a recognizable nostalgic mascot. That combination, paired with 13 million followers, was enough to make the promotion appear legitimate at a glance.
What Happened
Attackers altered Microsoft’s account in several ways before the compromise was detected.
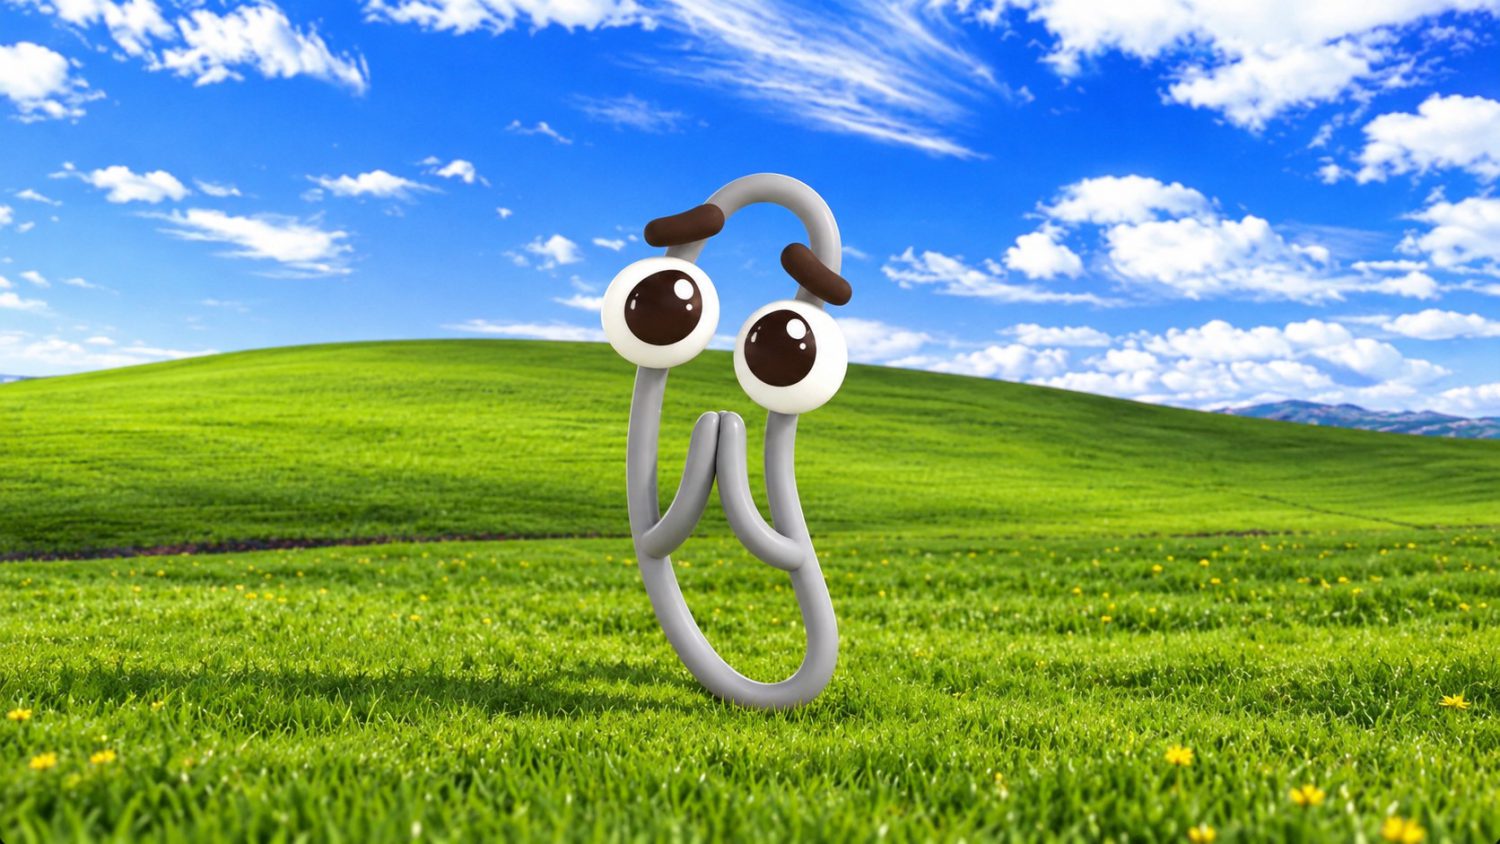
The attackers changed the profile image to the Clippy paperclip character, then followed and reposted content from @clippymsftcto, a Clippy impersonator account later suspended by X. A post appeared asking how many likes it would take to bring Clippy back, setting a target of 500,000 as a viral engagement hook. The token was promoted using the $MSFT ticker, presenting a false implication of a direct Microsoft connection.
The method of access, the identities of the attackers, and the financial impact on anyone who bought the token have not been established in available reporting.
Microsoft’s Response
Microsoft confirmed the unauthorized access, denied any connection to the token, and said the account has since been secured.
Microsoft spokesperson Brent Colburn confirmed the breach, according to SecurityWeek: “We have confirmed unauthorized access to our account on X, including posts that did not come from Microsoft.” A separate statement posted on X disavowed the token entirely. “To be clear, Microsoft does not support, endorse, sponsor, or authorize any cryptocurrency or crypto-related token,” according to the post, which PCMag reproduced before it was deleted.
Microsoft also said it intends to pursue legal action to remove the unauthorized token and related materials. The unauthorized posts have been removed, the account has been secured, and the incident remains under investigation. The reason the disavowal post was subsequently deleted remains unresolved.
What This Means for You
A verified account and a familiar logo are not proof that a company stands behind what it just posted.
Verified accounts can be compromised. If a brand you trust suddenly announces a cryptocurrency token, check its official website or press channels before acting on anything you see in a social feed.