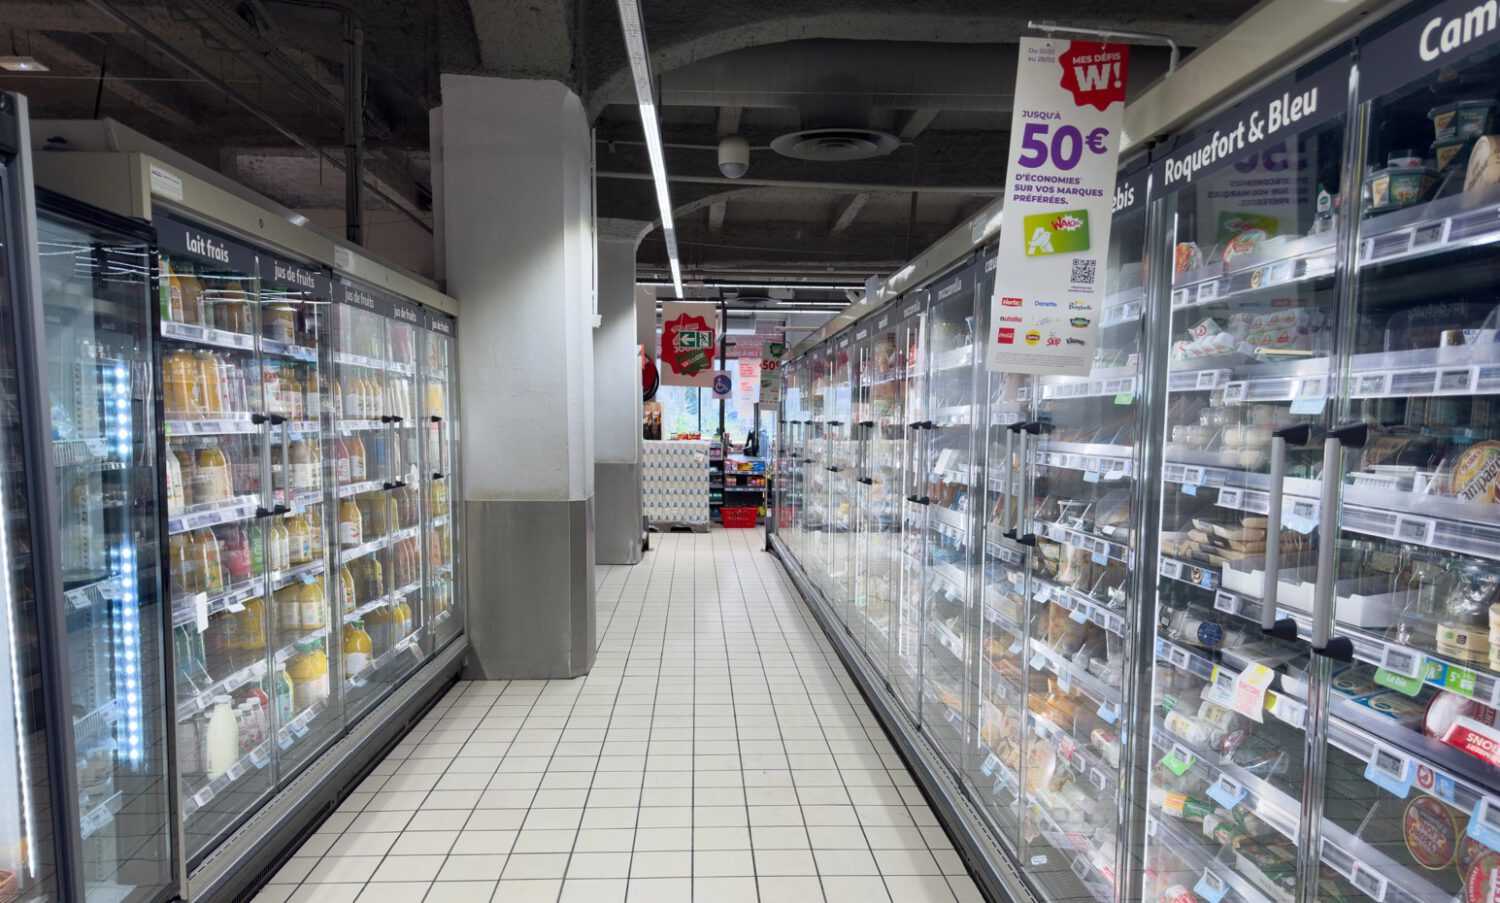
Refrigeration systems at more than 150 French supermarket locations were compromised overnight Oct. 11–12, 2026, according to early sector reporting. Some equipment reportedly reached temperatures of approximately 50°C, and stores discarded fresh and frozen stock the following morning, according to BFM TV, Le Parisien, and Libération.
This incident is not a typical data breach. Attackers reportedly manipulated the physical behavior of refrigeration equipment, converting remote software access into spoiled inventory and financial losses at stores across France.
Who Was Affected
Confirmed and unconfirmed chains span several of France’s largest grocery groups.
Coopérative U chief executive Dominique Schelcher publicly confirmed that a cyberattack had affected refrigeration installations at several stores and called for an investigation, according to Ouest-France. He described the incident as being of extreme gravity.
Sector reporting estimated roughly 150 Intermarché stores and fewer than 100 Coopérative U stores were impacted. Leclerc was also named in multiple reports. Carrefour, Monoprix, Metro, and independent retailers were mentioned in some outlets but had not been confirmed by those companies as of publication.
What the Attack Did
Attackers reportedly exploited remote management capabilities to force refrigeration equipment into continuous heating cycles.
Reports identify Danfoss refrigeration-management systems as the apparent technical target. Those systems monitor equipment remotely and can initiate automatic defrosting cycles when required.
Early reporting suggests attackers forced continuous defrosting and altered temperature settings in some units to approximately 50°C. That figure refers to the reported altered equipment setting or observed heating condition in affected locations, not necessarily the temperature of every product or every store. The intrusion method and access route had not been publicly confirmed as of publication.
The Financial Damage
Local figures hint at losses that could scale into the millions nationally, though no verified total was available.
Two stores in Alsace reported combined losses of approximately €270,000, according to Les Numériques: roughly €50,000 at an Intermarché in Haguenau and approximately €220,000 at a nearby Super U. Those figures suggest national losses could reach into the millions, though no verified national total was available at time of publication.
Stores discarded affected fresh and frozen inventory as a precaution to avoid selling potentially unsafe products. Intermarché communications cited by media instructed stores to prioritize replenishment.
What Remains Unconfirmed
Several critical details had not been established publicly as of Oct. 12, 2026.
- The total number of affected stores across all named chains
- The attackers’ identity, motive, and method of access
- Whether every affected retailer used the same Danfoss system or was compromised through the same vulnerability
- The final value of discarded products and total business losses
Investigation and Response
Authorities opened an inquiry while affected retailers worked to restore refrigeration operations.
Paris prosecutors reportedly confirmed that a cyberattack had occurred, according to Libération, though that report could not be independently verified from a prosecutorial statement in the available material. Coopérative U said its teams were working with refrigeration specialists to restore operations as quickly as possible. No attacker identity, confirmed motive, or customer data impact had been established publicly as of Oct. 12, 2026.
A New Kind of Consequence
This attack illustrates how remote access to industrial control systems can produce physical, not just digital, damage.
Remote access to industrial control systems has long been cited as a serious exposure point by cybersecurity professionals. Here, that access reportedly converted software manipulation into destroyed food and significant financial losses across multiple store locations.
Retailers and industrial control system operators may face pressure to reassess network segmentation, authentication protocols, anomaly detection, and manual override procedures for critical equipment.