A ransomware-as-a-service group called The Gentlemen added Nvidia to its dark-web leak site on November 18, 2026, setting a countdown of approximately 234 hours before an alleged data release. Nvidia had not confirmed any compromise at the time of reporting, and the listing itself provided no technical evidence of a successful intrusion.
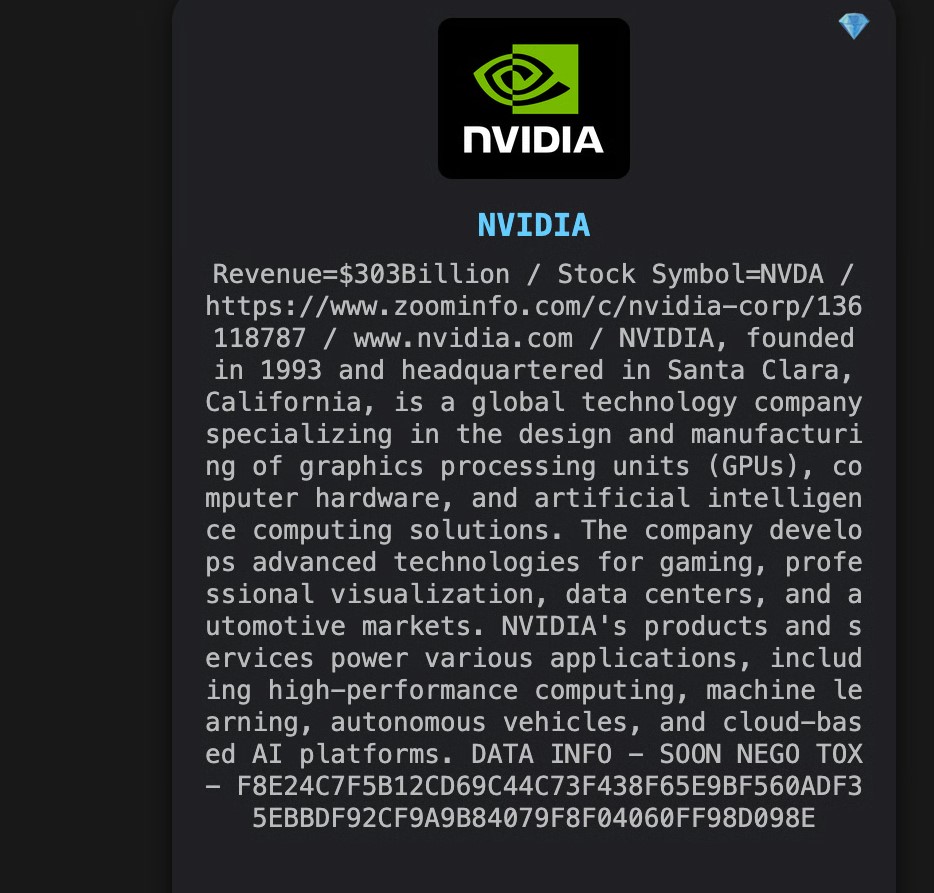
What the Listing Actually Showed
The posting contained no stolen files, no intrusion date, and no details identifying which part of Nvidia was allegedly affected.
According to reporting by technext24.com, the listing contained only basic public company details, a “SOON” notice, and a negotiation contact. It did not identify an affected business unit, specify an intrusion date, describe the type of data allegedly stolen, or include any sample files or documents.
A Countdown Is Not Evidence
Extortion timers are designed to pressure targets and generate media attention, not to demonstrate that an intrusion occurred.
A dark-web listing alone does not establish that a successful intrusion occurred. These countdown timers function as extortion pressure mechanisms; they are not technical evidence of system access or data theft.
Who Is The Gentlemen
Check Point research identifies The Gentlemen as one of the most active ransomware operations tracked globally through dark-web leak sites.
The Gentlemen operates as a ransomware-as-a-service syndicate, using affiliates or associated operators to conduct intrusions and deploy extortion tactics. Check Point reported more than 320 publicly claimed victims by April 2026, with roughly 240 of those listings appearing during 2026 alone.
Check Point also observed infrastructure associated with more than 1,570 likely corporate victims, indicating the operation’s broader scale. In its second-quarter 2026 reporting, Check Point tracked 269 victim postings from the group. That figure placed The Gentlemen among the most active ransomware operations tracked by Check Point through dark-web leak sites.
Scale Is Not a Substitute for Nvidia-Specific Evidence
The group’s established reach makes the Nvidia claim worth monitoring, but past volume cannot confirm a new intrusion.
The group’s established activity makes the claim worth monitoring. It does not, however, substitute for verified evidence linking The Gentlemen to Nvidia systems specifically.
What Verification Would Require
Three categories of evidence would meaningfully shift confidence in the claim, either strengthening or weakening it.
Verifiable sample files containing Nvidia-specific internal data, metadata, or document structure would provide stronger evidence than a bare listing. Incident-response findings or threat-intelligence indicators tied to Nvidia infrastructure would also materially strengthen the claim.
An official Nvidia statement, regulatory filing, customer notification, or security advisory confirming an incident would provide authoritative confirmation. If the countdown expires without credible Nvidia-related material appearing publicly, confidence in the claim would decrease. Nonpublication alone would not conclusively disprove an intrusion, but the listing would remain unsubstantiated.
Current Status
Nvidia had not issued any public statement or disclosure related to the alleged ransomware listing at the time of reporting.
Nvidia had not issued a public statement or confirmed a security incident at the time of reporting. The countdown, as reported by technext24.com, was set to expire approximately 10 days after November 18, 2026. Readers following developments should watch for sample file releases, independent technical findings, or any official Nvidia disclosure as the deadline approaches.