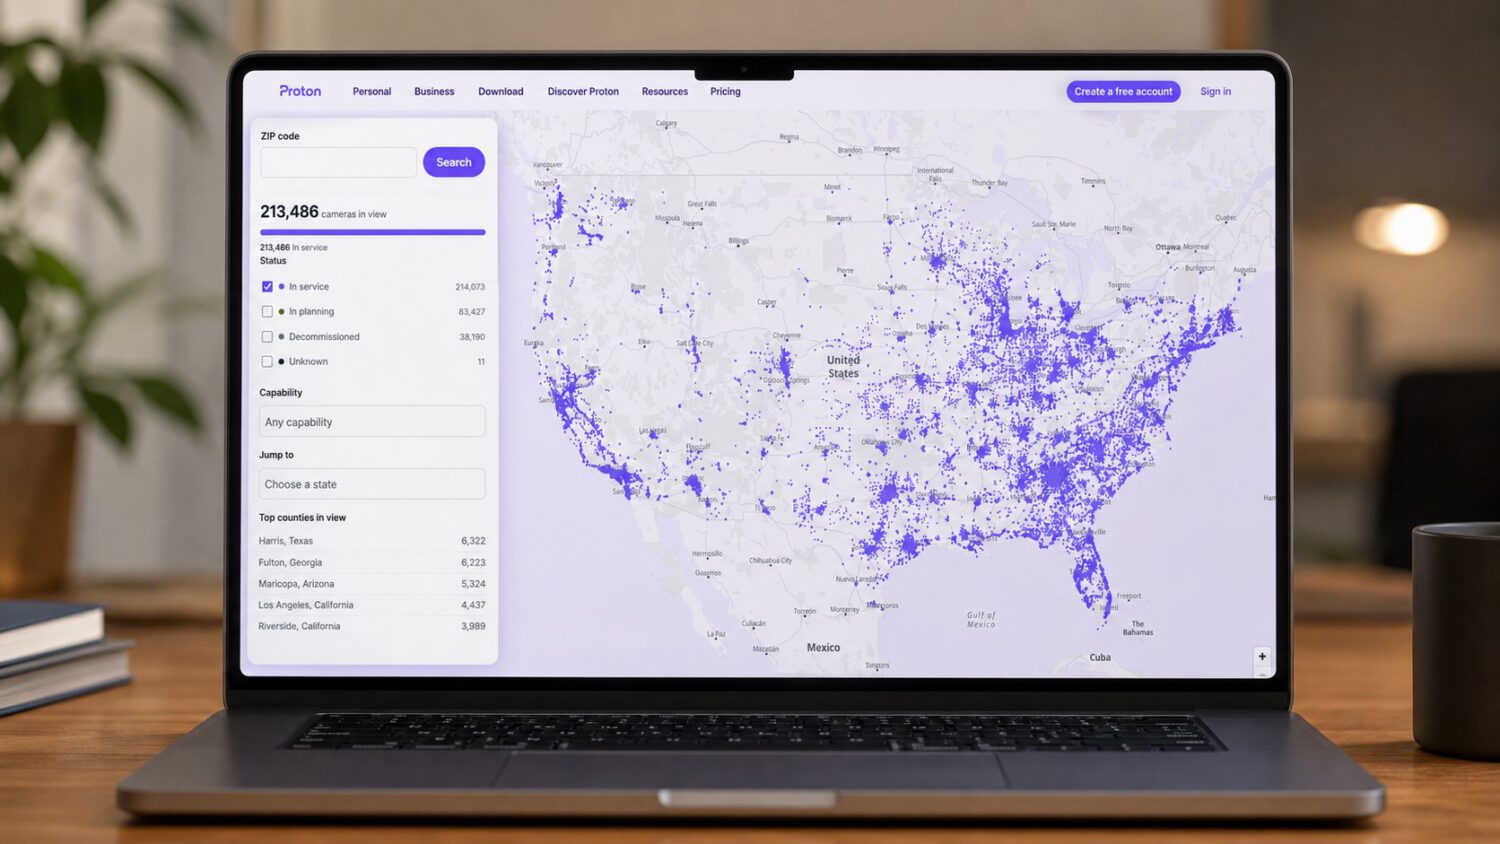
When a Flock Safety trademark complaint filed on behalf of Flock Safety sought to remove a public map of the company’s surveillance network, Proton moved the map to Swiss servers and kept it online. The privacy company’s decision preserves public access to an inventory that researcher Joshua Michael built from data he says Flock’s own website exposed.
Flock’s network reaches into hundreds of communities across the United States, and the map lets residents check whether that infrastructure operates near their homes, schools, or daily commutes.
What the Map Shows
The dataset covers more than 300,000 Flock-associated devices, and not all of them are cameras.
Proton’s hosted version draws from a December 2025 snapshot containing more than 170,000 cameras and more than 130,000 secondary units such as acoustic detectors, processing hardware, and networking equipment. Describing all 300,000 entries as cameras would misrepresent the dataset.
You can search the map by ZIP code to see what devices appear in your area, with equipment distinguished by model, including Falcon cameras and Picard processing units. Because the data reflects conditions as of December 2025, installations completed or removed after that date will not appear.
Flock has reportedly stated its network includes more than 120,000 cameras, while Michael’s dataset records a substantially higher camera count. The two figures may reflect different counting methods or dates, and the available reporting does not establish which is incorrect.
How the Data Was Obtained
A publicly exposed access token, requiring no login, gave a researcher a window into Flock’s device-location data.
In November 2025, Michael said he found that Flock’s website exposed an access token that required no login to obtain. That token allowed him to query ArcGIS, a third-party geospatial mapping platform Flock uses, and retrieve device-location data.
Michael reported the vulnerability to Flock before preserving the dataset in December 2025, though reporting conflicts on whether he separately notified Flock about the exposure. Flock subsequently appeared to address the exposure.
Flock rejects the characterization of these events as a hack or information leak. The company has stated publicly that it “has never been hacked, and there has not been a leak of Flock information.” Whether an unauthenticated, publicly obtainable token constitutes a security breach under applicable definitions remains contested. The available reporting confirms the exposure and retrieval but does not establish a definitive legal classification.
Trademark Complaint and Swiss Hosting
A brand-protection vendor filed a trademark complaint seeking the map’s removal, and Proton responded by hosting a copy on Swiss servers.
On September 24, 2026, Doppel, a brand-protection vendor working on Flock’s behalf, filed a trademark-infringement complaint. The complaint argued that the map’s use of the “FLOCK SAFETY” name could cause consumer confusion or harm. Proton republished the map after the original was targeted for removal, framing the decision as a commitment to keeping surveillance infrastructure publicly visible.
Proton’s legal position is that hosting the map on Swiss infrastructure limits the practical reach of a foreign takedown demand unless it is backed by a Swiss court order. That is Proton’s legal argument, not a judicial determination.
The episode raises a policy question that extends beyond this particular map. Whether companies can use trademark complaints or platform pressure to remove independently compiled information about the scale and operation of their own surveillance systems remains unresolved; no court ruling addressing this dispute appears in the available reporting.